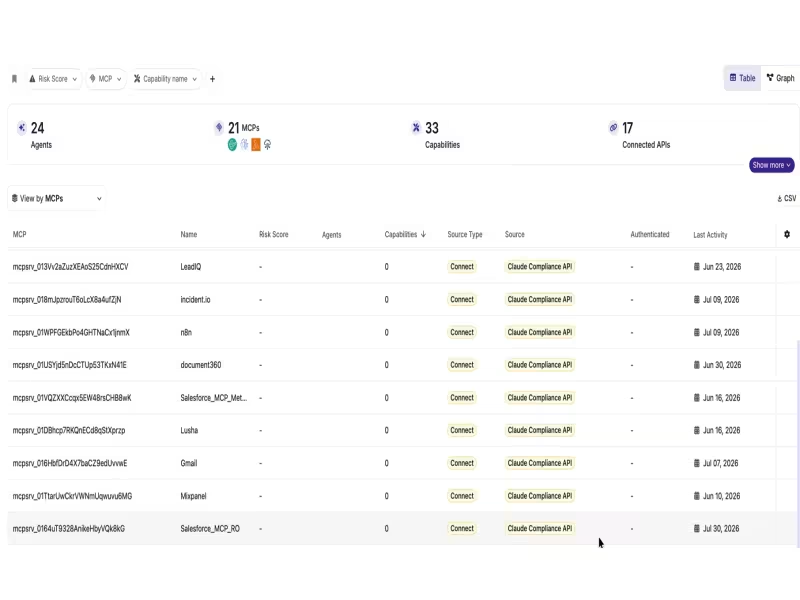
Palo Alto, Calif. – – September 29, 2026 -- Salt Security has launched Salt Claude Connect, an integration that gives security teams continuous, read-only visibility into Model Context Protocol (MCP) servers connected to their Claude Enterprise organization. The tool works with Claude's Compliance API to surface organization-managed MCP servers directly in a security team's Salt inventory.
Unsecured MCP servers nearly tripled in months, according to Trend Micro research
The number of MCP servers exposed on the public internet with no authentication or encryption climbed to 1,467, a near-tripling cited by Salt Security, with most hosted on major cloud providers and offering direct read access to underlying data. As enterprises scale AI adoption, MCP servers extend what AI environments can reach, and in large organizations they can be added faster than security teams can track them.
Salt Claude Connect surfaces server name, status, and lifecycle timing
The integration reads an organization's activity feed through Claude's Compliance API and automatically populates the Salt Agentic inventory with organization-managed MCP servers. Each entry is labeled by source and shows the server name, current status, and timestamp of its most recent lifecycle event -- added, updated, or removed. The inventory updates continuously as connectors change.
Integration requires only a single read-only scope, no access to prompts or content
Salt Claude Connect is built on least-privilege access, reading only MCP server lifecycle activity. It never sends prompts to Claude and does not read chat content, file content, or project data. The only data Salt stores is MCP server lifecycle events, and the integration cannot modify the Claude organization.
"MCP servers are one of the fastest-growing parts of the enterprise attack surface, and for most security teams, what's connected to their AI environment has been a blind spot they couldn't close,