San Francisco – October 13, 2026 -- Speakeasy, the AI control plane vendor, and Tailscale, the identity-first networking company, have partnered to let enterprises run the Speakeasy Model Context Protocol (MCP) gateway as a node on their own Tailscale tailnet. The integration is available now to Enterprise organizations on the Speakeasy AI Control Plane and is rolling out per organization.
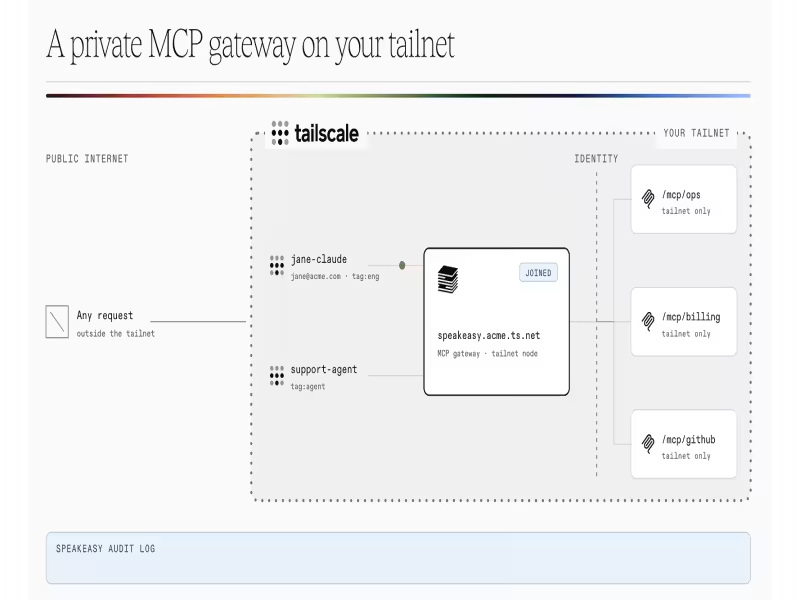
Speakeasy says many MCP deployments still rely on publicly reachable endpoints. Under the new setup, every MCP server is served on the tailnet, the public route can be closed entirely, and every request carries the Tailscale user and device it came from. The gateway that governs how AI agents reach company tools is reachable only from devices and identities the company's network already trusts.
Speakeasy adds MCP-specific policy on top of Tailscale connectivity
Tailscale supplies private, identity-aware connectivity across a company's people, devices, and services. Speakeasy layers on governance that codifies and enforces which actions agents may take. Speakeasy CEO Sagar Batchu said the company's thesis is that "every agent action requires the same controls as a human employee."
Tailscale customers have been adding agents to tailnets built for employees. For them, turning on Speakeasy means agent tool calls travel over the existing tailnet, with nothing new to deploy and no separate network to manage. Travis Perkins, Tailscale's VP of Global Customer Advocacy, said customers increasingly connect AI agents to the same systems employees already reach over Tailscale.
Polar restricts internal MCP servers to its tailnet
Polar, a payment infrastructure provider for software developers, has run MCP servers on Speakeasy since 2025. It began with an onboarding flow that configures a merchant's products and pricing from a plain-language description. The tools behind that flow can also issue refunds, change subscriptions, and read revenue data.
Polar's customer-facing MCP server stays public so merchants' agents can reach it. The servers its staff use for support and operations are set to private-only and answer on Polar's tailnet alone. CTO François Voron said the integration closed a gap in MCP-specific governance and auditing and gave Polar a single entry point it can control and audit.
Kubernetes operator places each organization's gateway on its own tailnet
The AI Control Plane runs on Kubernetes, and the Tailscale Kubernetes operator places each organization's MCP gateway on that organization's tailnet. An administrator authorizes Speakeasy with a scoped Tailscale OAuth client. The operator then provisions a highly available proxy and ingress for the organization. A per-organization attestor verifies each request and attaches the Tailscale identity before it reaches an MCP server. Credentials, nodes, and workloads are isolated between organizations.
The integration works with Speakeasy's MCP tunnels, which connect MCP servers inside a private network to the gateway over an outbound-only connection. Together, they let an agent reach a private MCP server without touching the public internet.
Tailscale is the first supported private network provider. Setup instructions are in Tailscale private network access documentation.