OX Security

Malicious LiteLLM 1.107.0 on PyPI Steals AI Keys, Installs RAT

Image
Malicious LiteLLM 1.107.0 on PyPI Steals AI Keys, Installs RAT

Global – October 29, 2026 -- A malicious version of LiteLLM, version 1.107.0, was published to PyPI on October 29, 2026. It bundles a credential-stealing infostealer with a remote access trojan (RAT), according to OX Security. It is the second hijacking of the AI gateway this year, and PyPI has since quarantined the release.

Malware hides in the wheel package, not the source repository

The attacker injected the code only into the wheel package, so a review of the repository or the clean source would show nothing wrong. Stolen data goes to litellm[.]dev, a domain the attacker bought that can pass for a legitimate LiteLLM address. In March, versions 1.82.7 and 1.82.8 were compromised in the TeamPCP campaign, but this attack used different tooling and infrastructure.
99.3% of Exposed PHP Hosts Unpatched 24 Hours After PHP2Shell Fix

Image
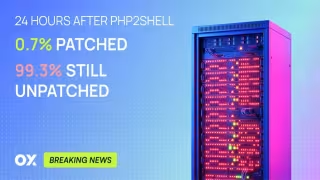
99.3% of Exposed PHP Hosts Unpatched 24 Hours After PHP2Shell Fix

GLOBAL – October 29, 2026 -- Only 14,151 of 1,974,890 measurable PHP instances in the affected version range showed a patched release 24 hours after PHP shipped emergency fixes for the PHP2Shell flaws, leaving 99.3% exposed, according to OX Security.

PHP released the fixes on October 21 for CVE-2026-109618 and CVE-2026-109619. Both are critical vulnerabilities that allow unauthenticated remote code execution in the PHP engine itself. Governments and security agencies urged organizations to patch immediately, and some organizations took systems offline.

93.6% of PHP Hosts Still Exposed to PHP2Shell Five Days After Fix

Image
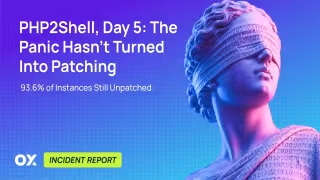
93.6% of PHP Hosts Still Exposed to PHP2Shell Five Days After Fix

Global – October 29, 2026 -- Five days after the PHP project shipped emergency fixes for the PHP2Shell flaws, 93.6% of measurable PHP instances remain exposed, according to OX Security scans run through October 26, 2026. That is roughly 15 of every 16 hosts the firm can measure.

The PHP project released the fixes on October 21 for CVE-2026-109618 and CVE-2026-109619. Together, the two critical flaws let an unauthenticated attacker execute code remotely inside the PHP engine. Security agencies issued urgent advisories, and some organizations took systems offline while assessing their exposure.

Shai-Hulud Malware Hijacks Tensorlake npm Package, 12K Weekly Downloads

Image
Shai-Hulud Malware Hijacks Tensorlake npm Package, 12K Weekly Downloads

Global – October 27, 2026 -- A malicious version of the tensorlake npm package (0.5.144), which draws about 12,000 weekly downloads, was published carrying Shai-Hulud malware, according to OX Security.

Malware wipes the host if a stolen GitHub token is revoked

The payload contains a kill-switch string, IfYouRevokeThisTokenItWillWipeTheComputerOfTheOwner, identical to the one used in the TanStack attack in May. Revoking the stolen GitHub token triggers rm -rf ~/ on Unix systems or Remove-Item on the Windows user profile.

OX advises isolating the machine from the network and killing the gh-token-monitor persistence before revoking anything. Any machine that installed tensorlake@0.5.144 should be treated as fully compromised, with all GitHub, npm, cloud, Vault, SSH and CI secrets rotated.

Apache Airflow SSH/SFTP Defaults Expose Pipelines to MITM, CVSS 8.1

Image
Apache Airflow SSH/SFTP Defaults Expose Pipelines to MITM, CVSS 8.1

Global – October 27, 2026 -- Apache Airflow's SSH and SFTP providers ship with host key verification disabled by default. Two High-severity vulnerabilities, CVE-2026-94134 and CVE-2026-94135, both rated CVSS 8.1, leave connections open to man-in-the-middle attacks, according to OX Security Research.

Both apache-airflow-providers-ssh and apache-airflow-providers-sftp are affected through version 6.0.1. Version 7.0.0 of each package fixes the flaw. The weakness is classified as CWE-322, key exchange without entity authentication.

Two PHP RCE Flaws Expose ~2 Million Servers; 99.99% Unpatched

Image
Two PHP RCE Flaws Expose ~2 Million Servers; 99.99% Unpatched

Global – October 27, 2026 -- Roughly 2,000,000 internet-facing PHP servers run versions affected by two critical remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, and 99.99% of identifiable servers remain unpatched, according to Shodan data cited by OX Security.

The PHP core team issued an out-of-band security release fixing both flaws in versions 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Shodan counts only servers that expose their PHP version, so the real total is likely higher.

69% of exposed servers run versions that will never get an official fix

About 1.37 million servers, or 69%, run old PHP versions outside vendor support. Only 245 servers showed a patched version as of the Shodan snapshot. Affected code spans all versions supporting session.upload_progress, from PHP 5.4.0 up to the unpatched releases.

OX Security Launches OX Cloud to Secure AI Agents in Production

New York – September 19, 2026 -- OX Security launched OX Cloud, a cloud security platform built to monitor AI agents that now operate autonomously in production environments, access sensitive data and call tools without human oversight.

OX Cloud adds AI Detection and Response to track agent behavior in real time

The platform's AIDR capability detects and governs AI activity across cloud and runtime environments as it happens, rather than relying on static configuration snapshots. Traditional cloud security tools identify misconfigurations, vulnerabilities and excessive permissions but cannot show security teams what an AI agent is actually doing once it operates inside an environment.