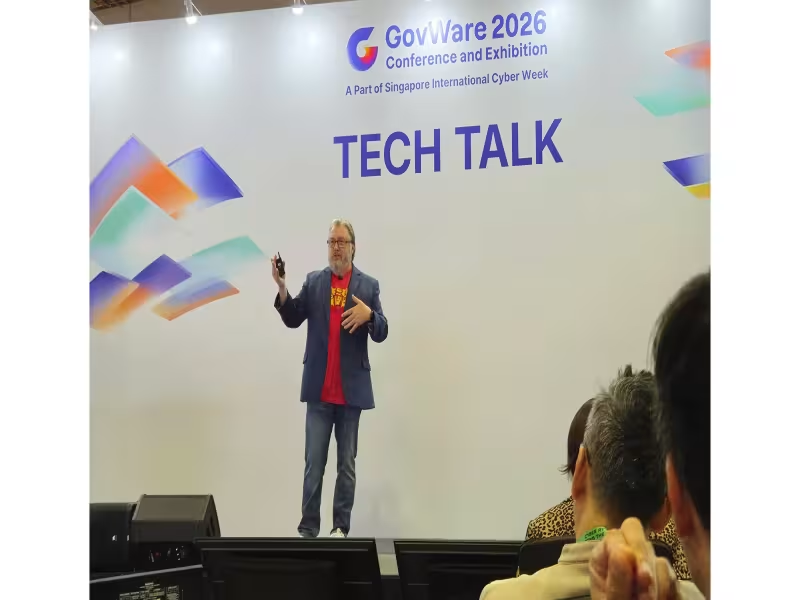
Singapore – October 14, 2026 -- Protiviti's February 2026 AI Pulse Survey found that 47% of large organizations have incomplete visibility into employees' use of AI tools, a gap Armor Founder and CEO Chris Drake cited at GovWare 2026 while arguing that CISOs should set conditions for AI adoption rather than ban it.
Drake said banning AI does not work and that ignoring it "is how the breach report gets written." In his Tech Talk Spotlights session, he said AI is already arriving through employees' browsers, productivity tools and machines, often without a separate security decision.
Drake says AI agents bypass the checkpoint CISOs had in the cloud era
During the cloud transition, security teams could assess a provider and influence which applications and data left the corporate environment. AI can skip that checkpoint. Depending on permissions, an agent can read files, send data and take actions, and the risk can travel over an allowed connection even when the firewall works as configured.
Drake pointed to visibility gaps in local virtual machines. Anthropic documents that host endpoint detection and response (EDR) cannot inspect activity inside Cowork's local VM. Docker documents that processes inside its local sandbox microVMs are invisible to the host. EDR alone cannot provide complete oversight, he said, and platform telemetry and network controls remain important.
CISOs need a written mandate and named risk owners, Drake says
Drawing on conversations across APAC, Drake described the pressure on CISOs who report to the CIO or CTO sponsoring an AI rollout. He urged them to agree on the business outcome, define what earns a yes and demand evidence that the controls and the business result work.
CISOs also need:
- a written mandate to approve, restrict or pause AI use;
- a named executive who owns each risk exception and its expiration date;
- an escalation path to the risk committee.
These decisions concern the conditions for adoption, not approval of every routine AI action.
Fourth-party AI risk extends exposure through suppliers
A vendor's use of another AI provider to process an organization's data introduces fourth-party risk. Organizations need evidence of which providers are involved, where data is processed, what is retained and which contractual protections apply. Drake said a useful, approved AI path can reduce employees' incentive to work around security, while discovery and supplier oversight remain essential.
Data classification becomes a must-have for automated AI policy
Drake said data classification has moved from nice-to-have to must-have. Organizations must know what their data contains, who owns it and how it may be used. Classification, ownership, permitted use and auditability form the basis for rules that systems can enforce automatically.
Organizations should then own the routing policy: approved external models when data policy permits, private execution when required. Task complexity, model capability, business needs and cost guide the choice among permitted options. AI can complete authorized work automatically, with records of the data accessed, policy decisions, models, routes, actions and outcomes, so the organization can reconstruct events without a person approving each step.
Armor built Sovereign AI after rejecting public AI services for customer data
Armor, a provider to regulated industries since 2009, was concerned about sending customer data through public AI services where controls and audit evidence could not meet its customer commitments. It built a governed AI platform for its own operations, now called Sovereign AI, and runs its business on it.
Drake's closing principles were: know the data, preserve model choice, own routing policies, control actions and demand full auditability. He called for powerful agents and their credentials to run in governed, isolated, auditable environments with scoped access, rather than on employees' laptops.
Before granting an AI tool access, he urged CISOs to ask what it can touch, where it can send and whether the organization can control what it does. His message: "Yes. With rules. With authority. With evidence."
Armor is demonstrating Sovereign AI at Booth A22 through October 15, with press and analyst briefings available on-site and virtually.