Cybersecurity

Target Sweeps RH-ISAC 2026 Awards; Crocs CISO Named Top Leader

Image
Target Sweeps RH-ISAC 2026 Awards; Crocs CISO Named Top Leader

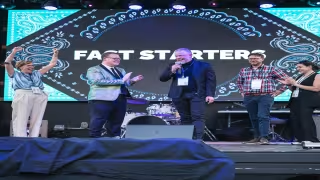
Vienna, VA – October 22, 2026 -- Target took three of the top honors at the 2026 RH-ISAC awards: Team of the Year, Cybersecurity Practitioner of the Year for senior threat intel analyst Chris De La Rosa, and a first-place finish in the Sharing & Collaboration Challenge team rankings. The Retail & Hospitality Information Sharing and Analysis Center announced the winners at its Member Celebration Dinner and Awards Ceremony on April 15 in Austin, Texas.

Crocs CISO Lena Taylor wins Peer Choice Award for CISO of the Year

Lena Taylor, CISO at Crocs, received the 2026 Peer Choice Award for CISO of the Year. The award goes to a thought leader whose experience adds strategic value to the wider community.
RH-ISAC Schedules 14 Cyber Workshops Across Three Regions in 2026

Image
RH-ISAC Schedules 14 Cyber Workshops Across Three Regions in 2026

Vienna, VA – October 22, 2026 -- The Retail & Hospitality Information Sharing and Analysis Center (RH-ISAC) has scheduled 14 confirmed in-person cybersecurity workshops across North America, Europe and Asia-Pacific for 2026, with a 15th planned for London in November.

Series opens in Singapore on 3 June and closes in Sydney on 11 November

The one-day events start in Singapore on 3 June, followed by Herndon, Virginia, on 11 June and Herzogenaurach, Germany, on 7 July. Stops in Natick, Massachusetts (29 July), Brampton, Canada (30 July), Bangalore, India (5 August), Louisville, Kentucky (13 August) and Richfield, Minnesota (18 August) complete the summer calendar.

The autumn run begins in Parsippany, N.J., on 16 September, then moves to Paris (25 September), Las Vegas (1 October), Vancouver (14 October), Atlanta (3 November) and Sydney (11 November). RH-ISAC has not yet released details for the London date.

RH-ISAC Schedules 2026 Regional Workshops Across Three Continents

Image
RH-ISAC Schedules 2026 Regional Workshops Across Three Continents

Vienna, VA – October 22, 2026 -- The Retail & Hospitality Information Sharing and Analysis Center (RH-ISAC) has announced the 2026 schedule for its Regional Workshop series, a global program hosted in key markets across North America, Europe and Asia-Pacific. The workshops bring cybersecurity practitioners together for in-person collaboration, threat intelligence sharing and professional development.

RH-ISAC and IANS publish 2026 CISO Benchmark Report on 1 April

The workshop announcement follows a run of releases from the group. On 1 April 2026, RH-ISAC and IANS released the 2026 CISO Benchmark Report. It examines how cybersecurity leaders in retail and hospitality are handling economic pressure, evolving threats and the rapid rise of artificial intelligence.

Saudi Firm NineTenths Joins ISASecure for OT Cybersecurity Push

Image
Saudi Firm NineTenths Joins ISASecure for OT Cybersecurity Push

DURHAM – October 21, 2026 -- NineTenths, a Saudi Arabia-based technology company founded in 2019, has joined ISASecure, the certification program that validates conformance to the ISA/IEC 62443 cybersecurity standards for industrial automation and control systems (IACS), the International Society of Automation (ISA) announced.

NineTenths ties its OT security services to ISA/IEC 62443

The company works in drones, robotics, infrastructure inspection, surveying and operational technology (OT) cybersecurity. Its clients span oil and gas, petrochemicals, energy, water and wastewater, manufacturing and other critical infrastructure.

NineTenths already uses ISA/IEC 62443 as the framework for its OT security services. Its capabilities are aligned to cybersecurity management systems, risk-based assessments, zones and conduits, industrial system security requirements and secure product development practices.

Crest Data Doubles Grafana Marketplace Portfolio to 25 Plugins

Image
Crest Data Doubles Grafana Marketplace Portfolio to 25 Plugins

San Francisco – October 21, 2026 -- Crest Data has added 15 commercial plugins to the Grafana Marketplace, more than doubling its portfolio to 25 as Grafana Labs moves the Marketplace to general availability at ObservabilityCON 2026.

Plugins query source systems via APIs without exporters or ingestion costs

All 25 plugins are native, agentless data source plugins that query their source systems through APIs. Crest Data states they require no exporters, no extra collection layer and no data ingestion costs. Each plugin ships with pre-built dashboards and was built in partnership with Grafana Labs.

The new plugins cover cloud security, virtualization and data protection platforms. IT, platform and security teams can monitor these systems in Grafana alongside existing telemetry rather than switching between separate vendor consoles.

Corsha Launches Folio to Auto-Map Live OT Networks for Compliance

Image
Corsha Launches Folio to Auto-Map Live OT Networks for Compliance

WASHINGTON – October 21, 2026 -- Corsha has launched Folio, a module for its Industrial Identity Security Platform that automatically generates and updates maps and documentation of how operational technology (OT) systems are connected and communicating, replacing manual assessments that the company says take weeks.

Folio draws on live network and access data captured by Corsha Gatekeepers. It records which machines are communicating, when, why and how, and produces derived hardware lists, real-time connection maps and Microsoft Visio data flow diagrams. The outputs are designed for IEC 62443, NERC CIP and Zero Trust frameworks.

Folio targets documentation gaps that slow OT compliance and incident response

Corsha says OT documentation is often missing or has drifted too far from the running environment to be useful. Compliance artifacts built through manual assessments are frequently incomplete or inaccurate, according to the company.

QKS Group Names Radware Leader in Q4 2026 Bot Management SPARK Matrix

Image
QKS Group Names Radware Leader in Q4 2026 Bot Management SPARK Matrix

PUNE, India – October 21, 2026 -- QKS Group named Radware a technology leader in its global SPARK MatrixTM: Bot Management, Q4 2026, with strong ratings across technology excellence and customer impact. The study ranks leading vendors and assesses market dynamics, major trends, vendor landscape and competitive positioning.

Radware shifts bot detection from static signatures to intent analysis

Sofia Ali, Principal Analyst at QKS Group, said Radware has moved detection away from static signatures and score-based rules toward intent-driven analysis of automation behavior. Its engine combines three elements in one self-learning framework: pre-emptive blocking through the ERT Active Attackers Feed, AI-based behavioral analysis across hundreds of signals, and real-time signature generation. According to Ali, the framework catches evasive, human-like bots with less manual tuning.

Industrial Defender Adds Network Monitoring, Risk Signal to OT Platform

Image
Industrial Defender Adds Network Monitoring, Risk Signal to OT Platform

Orlando – October 20, 2026 -- Industrial Defender has released a platform update that adds internal network security monitoring (INSM) and a remediation tool called Risk SignalTM, targeting utilities that must comply with the FERC-approved NERC CIP-015-1 standard.

The standard requires entities with high and medium impact BES Cyber Systems to monitor internal network traffic, detect and evaluate anomalies, and retain and protect the resulting data.

INSM learns device baselines and flags deviations

Built into the existing platform, the INSM solution learns each device's baseline communications. It flags new connections, unexpected protocols, anomalous traffic volume and unknown devices communicating.

Each anomaly is correlated with the asset data Industrial Defender maintains, including configuration changes, vulnerabilities and risk score. Operators can see immediately what a network change means to operations, the company said.

Nationwide's Todd Lukens Named to OhioX Cyber25 Security List

Image
Nationwide's Todd Lukens Named to OhioX Cyber25 Security List

Ohio – October 20, 2026 -- Todd Lukens, chief technology and information security officer at Nationwide, has been named to the inaugural Cyber25 list from Ohio Tech News and OhioX, which honors 25 cybersecurity leaders protecting Ohio's businesses, hospitals, schools and critical infrastructure.

Selection criteria weigh two years of Ohio-linked results

Honorees were chosen on four criteria: real-world impact, demonstrated leadership, a meaningful Ohio connection, and work completed or significantly advanced during the past two years.

Lukens oversees eight security and technology functions at Nationwide

Lukens has more than two decades of experience in cybersecurity and technology leadership. His remit covers Cybersecurity, Information Risk Governance, Continuity and Crisis Management, Infrastructure, Technology Operations, Development Platform Engineering, Enterprise Digital Platform, and Protective Services.

CloudFit: CMMC Phase II Pause Leaves DFARS, NIST Duties Intact

United States – October 20, 2026 -- CloudFit said the Department of War's pause on parts of the CMMC rollout does not change cybersecurity obligations for the more than 220,000 organizations in the Defense Industrial Base (DIB) that are entrusted with protecting Controlled Unclassified Information (CUI).

CloudFit says DFARS and NIST requirements remain in force

The company said the implementation timeline for portions of CMMC may be changing, but obligations to safeguard sensitive information under DFARS and NIST requirements have not been paused. It added that cyber threats have not paused either.

Cost and complexity block adoption across the DIB

CloudFit argues that compliance mandates alone will not secure the DIB. It says many companies have had to choose between expensive custom implementations, delaying security investments, or attempting compliance on their own. In its view, that model does not scale to the size of the DIB.