Cybersecurity

Real-Time MFA Phishing Turns One Click Into Org-Wide Breach

Global – October 20, 2026 -- Attackers are now capturing valid multi-factor authentication (MFA) codes in real time, so a single phishing click can give them full account access and a path into an entire organization, according to Chris Bentkowski, Service Engineer at CloudFit.

Fake login pages harvest passwords and live MFA codes

The typical attack starts when a user clicks a malicious link and lands on a fake login page that mimics a trusted application. The user enters a username and password, then a valid code from an authentication app. The attacker can then complete authentication, capture session details and potentially reconfigure or take control of MFA mechanisms. Bentkowski calls the technique MFA phishing, or token/session capture.
Scientific Games' Atlanta Plant Earns Top WLA Security Certification

Image
Scientific Games' Atlanta Plant Earns Top WLA Security Certification

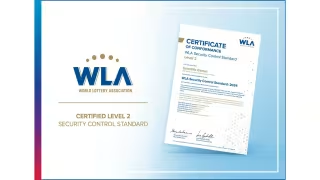
Atlanta – October 19, 2026 -- Scientific Games' U.S. instant scratch game production facility, which serves nearly every U.S. state lottery, has achieved Level 2 certification under the World Lottery Association Security Control Standard 2024 (WLA-SCS:2024). Level 2 is the highest certification level for lottery suppliers under the standard.

The plant, located at the company's global headquarters in metro Atlanta, is the world's largest lottery scratch game production facility. It has held WLA security certification since 2011.

Standard combines ISO 27001:2022 with lottery-specific integrity controls

WLA-SCS:2024 Level 2 merges the ISO/IEC 27001:2022 information security requirements with lottery-specific security and integrity controls set by the WLA. It specifies the practices needed for a security management structure that protects the integrity, availability and confidentiality of information critical to a lottery operator.

MiniOrange CEO to Pitch Identity-First Security at ASPIRE 2026

Image
MiniOrange CEO to Pitch Identity-First Security at ASPIRE 2026

Hoboken – October 19, 2026 -- MiniOrange CEO Anirban Mukherji will tell small and midsize business executives on October 21, 2026, that stolen credentials, not malware, are now the primary entry point for attacks, as eMazzanti Technologies hosts its annual ASPIRE 2026 conference at the Microsoft Conference Center in New York City's Times Square.

Mukherji targets six operational and compliance pain points

His session will cover password fatigue, application sprawl, remote workforce security, regulatory compliance requirements, cyber insurance mandates and third-party access management.

He will present five technologies as ways to reduce risk while simplifying access to business applications: multi-factor authentication (MFA), single sign-on (SSO), adaptive authentication, identity governance and privileged access management.

eMazzanti Technologies Named NJBIZ 2026 Business of the Year Finalist

Image
eMazzanti Technologies Named NJBIZ 2026 Business of the Year Finalist

Hoboken – October 19, 2026 -- eMazzanti Technologies, the Hoboken-based cybersecurity and managed services provider founded in 2001, has been named a finalist in the NJBIZ 2026 Business of the Year Awards, with honorees to be recognized at a live event on Dec. 8 at The Marigold in Somerset.

Panel of past honorees selects finalists on growth and innovation criteria

An independent panel of judges made up of previous program honorees chose the finalists. The program recognizes organizations for sustained growth, innovation, leadership and positive impact on New Jersey's business community.

Nexcess Adds Acronis EDR as Server Security Add-On

Image
Nexcess Adds Acronis EDR as Server Security Add-On

Lansing – October 19, 2026 -- Nexcess has made Acronis Endpoint Detection and Response (EDR) available from October 19, 2026 as an add-on for any eligible server on its managed cloud platform, bundling real-time threat monitoring into the hosting relationship.

Nexcess targets AI-accelerated attacks with continuous server monitoring

Nexcess argues that artificial intelligence has removed two barriers to sophisticated attacks: the need for deep engineering expertise and months of patient reconnaissance. Acronis EDR is its response, monitoring how programs behave on a server, flagging activity that looks like an attack and keeping a record of what happened.

The company positions EDR as a step beyond antivirus, which blocks known threats. EDR instead monitors activity continuously, identifies suspicious patterns, and contains threats in real time. Customers receive the details and tools to respond.

Bloomberg TV to Air Discoveries Today Episode on AI Security, Oct. 24

Jupiter, Florida – October 19, 2026 -- Bloomberg Television will broadcast a Discoveries Today episode hosted by Daymond John on Saturday, October 24, 2026, at 8:00 p.m. ET, covering four segments: disability support services, AI security governance, automotive retail marketing and behavioral healthcare.

AI governance segment focuses on zero-trust security for critical infrastructure

The security segment addresses zero-trust architecture, operational technology protection, and verifying AI identities, permissions and actions before they can affect sensitive systems. It covers how AI governance is being designed for critical infrastructure and regulated environments. It also covers how AI governance software is being aligned with federal security requirements and frameworks. The segment stresses accountability and verifiable decision-making as ways for organizations to keep control over increasingly autonomous technologies.

ShinyHunters Claims Data Theft From 300 Oracle PeopleSoft Instances

Image
ShinyHunters Claims Data Theft From 300 Oracle PeopleSoft Instances

Global – – October 19, 2026 -- The ShinyHunters extortion gang claims it has stolen data from 300 Oracle PeopleSoft instances across more than 100 organizations, BleepingComputer reported on 10 June 2026. The group says it is targeting both cloud and on-premises deployments of the enterprise suite, which large organizations use for HR, payroll, finance, supply chain, procurement and student administration.

Education sector bears most of the attacks

Most affected organizations are in education, and many were previously extorted by the same actor. ShinyHunters confirmed Nottingham University as a victim and has already published its data on the group's leak site. The university has acknowledged a cybersecurity incident in a statement.

Icarus Claims Klue Breach; Salesforce Disables Integrations

Image
Icarus Claims Klue Breach; Salesforce Disables Integrations

Global – – October 19, 2026 -- Salesforce has disabled all Klue integrations after the threat group Icarus claimed on 19 June 2026 to have exfiltrated customer data through the market intelligence platform's Salesforce connection. Matching data points give high confidence that Icarus is behind the supply chain attack, according to the source analysis.

Attackers pushed token-stealing code on 11 June

The compromise began on 11 June, when anomalous behavior occurred in a system connecting Klue's various integrations. Attackers pushed a code update that could collect the OAuth tokens customers use to connect Klue to their own systems. Klue noticed the activity on 12 June, including unusual network connections to IP addresses the actor used to run commands on its backend servers.

On 13 June, Klue staff disabled the remote access, removed the token-theft code and sent customers a general alert. The alert did not say which customers were affected.

Wiz Finds GitHub Flaw Letting One git push Run Code on Servers

Image
Wiz Finds GitHub Flaw Letting One git push Run Code on Servers

Unspecified location – October 19, 2026 -- Wiz Research found a critical vulnerability, CVE-2026-3854, that let any authenticated user execute arbitrary commands on GitHub's backend servers with a single git push command, and 88% of GitHub Enterprise Server instances remained vulnerable at the time of disclosure.

Wiz Research uncovered the flaw on 20 April 2026 in GitHub's internal git infrastructure. It affects both GitHub.com and GitHub Enterprise Server (GHES). The exploit requires only a standard git client.

GitHub.com is fully mitigated; GHES versions up to 3.19.1 stay exposed

GitHub has fully mitigated the issue on GitHub.com, and users there need to take no action. GHES versions up to and including 3.19.1 are vulnerable.

Fixed versions are 3.14.24, 3.15.19, 3.16.15, 3.17.12, 3.18.6 and 3.19.3. GitHub released patches for all supported GHES versions, and administrators are urged to upgrade immediately.

NFCShare Android Trojan Hides in GitHub, Breaks APK Extractors

Image
NFCShare Android Trojan Hides in GitHub, Breaks APK Extractors

Italy – October 19, 2026 -- A newer wave of the NFCShare Android banking trojan, active since 14 May 2026, ships APKs with malformed ZIP paths that can break automated extraction tools, D3 Labs researchers reported.

Campaign shifts from Deutsche Bank lure to Italian and European brands

NFCShare first spread as a malicious APK through a phishing flow impersonating Deutsche Bank. The newer wave impersonates Italian and European banking brands and originates from a phishing site mimicking Intesa Sanpaolo. The malware shows a fake card-verification screen, asks victims to hold a payment card near the phone, collects the card PIN and sends NFC-derived card data to a WebSocket endpoint.

Core NFC logic unchanged, operations hardened

D3 Labs found the NFC and exfiltration logic largely unchanged. The changes are operational: more frequent APK rebuilds, brand rotation, URL shorteners, a new C2 endpoint and a 10-DEX layout.