Cybersecurity

Retail, Hospitality Face AI Vishing as 62% of Breaches Involve People

Image
Retail, Hospitality Face AI Vishing as 62% of Breaches Involve People

Global – October 19, 2026 -- About 62% of security breaches still involve the human element, according to the 2026 Verizon Data Breach Investigations Report. That figure is pushing retail and hospitality security teams to replace annual compliance videos with human risk management (HRM), which aims to change how employees respond to attacks in real time.

Scattered Spider uses AI voice cloning to turn help desk calls into footholds

Threat groups such as Scattered Spider scrape professional networks like LinkedIn to map organization charts and identify help desk staff and executives to impersonate. They then place high-pressure calls with AI-cloned voices, posing as locked-out employees. The goal is to get agents to reset a password and enroll multi-factor authentication (MFA) on a device the attacker controls.
ClickLock Stealer Hits 100+ macOS Victims in 33 Countries

Image
ClickLock Stealer Hits 100+ macOS Victims in 33 Countries

Europe – October 19, 2026 -- A new macOS infostealer dubbed ClickLock Stealer has targeted at least 100 victims across 33 countries since May 2026, with more than 50% of them in Europe, according to Group-IB Threat Intelligence.

Group-IB reported on 9 June 2026 that a malicious shell script uploaded to VirusTotal was assessed as a new modular stealer, likely distributed through ClickFix phishing pages. The operation has been active for approximately two months and relies on compromised WordPress domains and Telegram infrastructure. The malware needs no elevated privileges or exploits to execute.

MAG Breach Exposes Data of 8.7 Million Airport Customers

Image
MAG Breach Exposes Data of 8.7 Million Airport Customers

Manchester – – October 19, 2026 -- Manchester Airports Group (MAG) has disclosed that an unauthorized third party accessed customer data on approximately 8.7 million people across Manchester, London Stansted and East Midlands airports.

Hackers obtained contact details and vehicle registration numbers

The affected data relates to parking, lounge and fast-track bookings and in-airport Wi-Fi sign-ups. The attackers obtained email addresses, phone numbers, vehicle registration numbers and postcodes.

The attack took place during peak summer travel, as millions of families were flying back into the UK before the school year. Airport operations and flights were not disrupted.

MAG says most affected customers lost only their email address

The affected systems did not store bank or payment details. According to MAG, most of the 8.7 million customers lost only their email addresses, and the impact varies by the services each person used.

ICANN87 Opens in Indonesia With 200+ Sessions on DNS Security

Image
ICANN87 Opens in Indonesia With 200+ Sessions on DNS Security

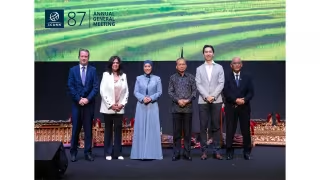
Bali – October 19, 2026 -- ICANN87, the first ICANN public meeting held in Indonesia, opened with more than 200 working sessions on DNS Abuse mitigation, Domain Name System security and the New gTLD Program.

The six-day meeting is co-hosted by the Indonesian Internet Domain Name Registry (PANDI). Indonesia's Ministry of Communication and Digital Affairs and the Bali Provincial Government are supporting it. Attendees include government representatives, businesses, technical experts and civil society.

ICANN leadership pushes for tighter links between strategy and execution

ICANN President and CEO Kurtis Lindqvist said the organization must connect strategy, prioritization, budgeting and implementation more clearly. He said ICANN org "must turn those solutions into effective action" developed by the community.

Trend Micro Offers Up to ¥10B in Credits for Japan Cyber Push

Image
Trend Micro Offers Up to ¥10B in Credits for Japan Cyber Push

Tokyo – October 19, 2026 -- Trend Micro (TSE: 4704) plans to make available up to ¥10 billion in TrendAI Flex licensing credits under a new Japan Cyber Resilience Initiative, as publicly disclosed cyber incidents in Japan hit 607 in the first nine months of 2026, already above the 594 recorded for all of 2025.

The incident tally comes from TrendAI threat research and is current as of October 9, 2026. Trend Micro notes the figure may change as incidents are disclosed retroactively and further cases are added.

HKU, GCSA Launch Joint AI and Cybersecurity Research Centre

Image
HKU, GCSA Launch Joint AI and Cybersecurity Research Centre

Hong Kong – October 19, 2026 -- The University of Hong Kong (HKU) and the Global Cybersecurity Alliance (GCSA) have jointly established the Centre for AI and Cybersecurity Research, with four defined research directions spanning large language model security, automated threat defence, frontier-technology risk and global AI security standards.

Professor Ho Chen, Chair of Cybersecurity at the HKU School of Computing and Data Science, will serve as Acting Director. The Centre will bring together researchers from HKU, GCSA and international partner institutions. It will also engage experts in artificial intelligence, cybersecurity and technology governance for research and advisory roles.

Coalition: Cyber Insurer Paid $315M in Claims in 2025, Rebuts Myths

Image
Coalition: Cyber Insurer Paid $315M in Claims in 2025, Rebuts Myths

United States – October 17, 2026 -- Coalition says policies it provided paid more than $315 million in cyber claims in 2025. The insurer is urging brokers to counter the belief that cyber insurance does not pay claims, an objection it says can stall coverage decisions.

Zero-indemnity closures reflect early intervention, Coalition argues

The National Association of Insurance Commissioners (NAIC) reported that 26% of cyber claims in 2025 closed with indemnity payments. Verizon reported a recorded pay-out on 55% of 2025 claims. Coalition says critics read claims closed without an indemnity payment as denials, when many reflect incidents contained early.

BEC Attackers Argue Inside Inbox Rule Names, Coalition Finds

Image
BEC Attackers Argue Inside Inbox Rule Names, Coalition Finds

Global – October 17, 2026 -- Coalition Incident Response (CIR) has documented rival Business Email Compromise (BEC) attackers using the names of inbox rules as a chat channel inside the same compromised mailbox, and says the exchanges expose gaps in default email platform security.

Two intruders negotiate and fight through rule names

Abusing inbox rules to evade detection (MITRE ATT&CK T1564.008) is a widespread tactic. Attackers use it to hide, redirect or forward emails containing keywords such as "invoice" or "confidential." In one CIR investigation, an attacker aware of a second intruder appeared willing to cooperate so that neither ruined the payout. In another incident, two actors fought over an inbox in a prolonged argument recorded as a sequence of rule names.

Coalition Rebuilds MDR Around Millisecond Automation With Wirespeed

Image
Coalition Rebuilds MDR Around Millisecond Automation With Wirespeed

Global – October 17, 2026 -- Coalition says its Wirespeed platform cuts alert noise by 99.99% before any alert reaches a customer queue, replacing analyst-driven managed detection and response (MDR) with automated verdicts and containment in milliseconds.

Coalition acquired Wirespeed to address a bottleneck it attributes to legacy MDR: human analyst capacity. Adding headcount widens the alert queue and raises prices for customers without speeding up response, the company argues. Forrester Research recognized Coalition in its report The Managed Detection And Response Services Landscape, Q3 2026.

Citrix Confirms Two NetScaler Zero-Days Exploited, 36 Hours Late

Image
Citrix Confirms Two NetScaler Zero-Days Exploited, 36 Hours Late

Global – October 17, 2026 -- Citrix confirmed on September 27 that two critical NetScaler zero-day vulnerabilities, each scoring 9.5 in severity, were exploited in the wild. According to cyber insurer Coalition, the vendor's public communications lagged the first reports by at least 36 hours.

Two flaws allow remote code execution on unpatched NetScaler appliances

CVE-2026-88771 is a critical remote code execution (RCE) flaw that lets an unauthenticated attacker run arbitrary commands. CVE-2026-88772 is a memory overflow vulnerability that can lead to RCE or a denial-of-service condition. The Citrix patch also fixes six other flaws, bringing the total to eight.

NetScaler provides remote access to internal applications and desktops and is often exposed directly to the internet, which makes it a frequent target. Enterprises across all industries use it.