Cybersecurity

Coalition Sends 49 Zero-Day Alerts as Patch Tuesday Hits 569 Flaws
Image
Coalition Sends 49 Zero-Day Alerts as Patch Tuesday Hits 569 Flaws

Global -- Coalition sent just 49 Zero-Day Alerts (ZDAs) between May 1 and August 1, 2026, even as Microsoft's July Patch Tuesday swelled to 569 vulnerabilities, and 94% of its policyholders did not receive a single one.

Microsoft's Patch Tuesday count nearly triples in one month

June's Patch Tuesday set a record with 206 vulnerabilities. July's release nearly tripled that to 569. Before Microsoft adopted multi-model AI for vulnerability discovery, it typically shipped around 100 fixes a month. Windows said in July that it would apply AI across security analysis to find flaws earlier and at greater scale, which Coalition says likely contributed to the jump.

Attackers are also moving faster. Anthropic disclosed earlier this year that Mythos could create working exploits for newly discovered vulnerabilities in hours rather than weeks.
ConnectWise Probes Unauthorized Access to Microsoft 365 Backup App

Image
ConnectWise Probes Unauthorized Access to Microsoft 365 Backup App

Global – October 17, 2026 -- ConnectWise is investigating attempted unauthorized access to its Cloud Backup for Microsoft 365 service, formerly SkyKick Cloud Backup, after disclosing the incident on October 16. The company says containment measures are in place and it has no indication that partner backup data was accessed. The investigation is ongoing.

Community reports allege attacker used the backup app's Entra credentials

Separate reports in the MSP community describe an attacker using the backup service's Microsoft Entra application to enter customer tenants and exfiltrate email, SharePoint and Teams data. ConnectWise has not confirmed these reports.

ConnectWise published indicators tied to the suspicious authentication activity: source IP 144.172.64.128 and the user agents Python-urllib/3.12 and python-requests/2.31. The company notes that their presence alone does not confirm compromise.

Brightmoor Hospice Notifies Patients After Email Account Breach

Griffin -- Brightmoor Hospice, LLC began mailing breach notifications on October 16, 2026, after two employee email accounts were accessed without authorization and found to contain protected health information of certain patients.

Unauthorized access lasted two days in March 2026

Brightmoor discovered suspicious activity on or around March 25, 2026. Third-party specialists determined that the two accounts were accessed between March 24 and March 25, 2026. The company secured the accounts immediately and began reviewing their contents.

Review confirmed patient data on August 18, 2026

Brightmoor determined on August 18 that protected health information was present in the accounts. It then reviewed internal records to locate addresses for potentially affected individuals. Mailing began 59 days later. The company has not stated how many individuals are affected.

Eventide Earns SOC 2 Type 1 for Cloud Recording and AI Tools

Image
Eventide Earns SOC 2 Type 1 for Cloud Recording and AI Tools

Little Ferry, N.J. – October 16, 2026 -- Eventide Communications has completed an independent SOC 2 Type 1 examination covering the security and availability of its cloud-based mission-critical recording and analytics solutions, giving public safety buyers third-party evidence of its controls.

A-LIGN audits cloud environment against Security and Availability criteria

The examination was performed by A-LIGN, a cybersecurity compliance and audit firm. It evaluated controls against the Security and Availability Trust Services Criteria and included an assessment of relevant HIPAA/HITECH safeguards.

The scope covers Eventide's broader cloud environment and the controls supporting its cloud-based solutions. These include Critical Insights AI™ and the cloud-hosted and virtualized NexLog® DX-Series recording solutions.

Keeper Security Links Tenable Cloud Findings to Instant Remediation

Image
Keeper Security Links Tenable Cloud Findings to Instant Remediation

Chicago – October 16, 2026 -- Keeper Security has launched native integrations with Tenable that let cloud security teams remediate findings in seconds rather than the days or weeks manual workflows typically take, and that move static scan credentials out of Tenable policies into Keeper.

The integrations are available now to Keeper customers with active KeeperPAM licenses.

Tenable findings feed directly into Keeper's remediation engine

Cloud findings from Tenable now go straight into Keeper's remediation engine. Security teams can rotate credentials, enforce Just-In-Time (JIT) access and remove standing privileges without leaving the Keeper platform. Once remediation is complete, Keeper notifies Tenable and moves the finding to resolved status, with no manual follow-up or ticket management.

CTM, Huawei Plan Quantum-Safe, Built-In Security for Macao Network

Image
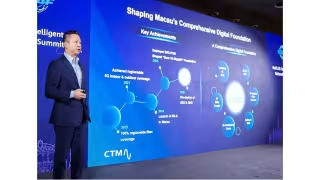
CTM, Huawei Plan Quantum-Safe, Built-In Security for Macao Network

Vienna – October 16, 2026 -- Macao carrier CTM and Huawei have jointly developed a target IP architecture that integrates quantum key distribution (QKD) with communication networks, as CTM outlined a plan to make security a built-in network function rather than an edge-firewall add-on.

CTM presented the roadmap in a keynote at Network X 2026. The operator is moving its network from a traditional connectivity pipe to what it calls intelligent, deterministic and secure infrastructure, aimed at speeding up enterprise digital transformation in Macao.

CTM adds AGW and AI BNG capabilities to steer traffic and cut bandwidth costs

CTM is introducing AGW and AI broadband network gateway (BNG) capabilities to give the network service awareness and dynamic scheduling. The system steers traffic to optimal paths, with the stated goals of improving user experience and lowering international bandwidth costs.

Advantech, DEKRA Sign MOU as EU CRA Compliance Pressure Builds

Image
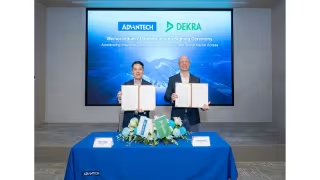
Advantech, DEKRA Sign MOU as EU CRA Compliance Pressure Builds

Taipei – October 16, 2026 -- Advantech's AFE-E630 industrial edge system has received an Attestation of Conformity from DEKRA for IEC 62443-4-2 SL2 requirements, the first result of a new memorandum of understanding (MOU) between the two companies on industrial cybersecurity compliance.

The MOU, announced as the EU Cyber Resilience Act (CRA) enters its implementation phase, targets industrial equipment and Edge AI products bound for global markets. The partners aim to help system integrators and end customers meet CRA requirements and international standards such as IEC 62443, cut compliance risk and shorten time to market.

Cyfendo Targets SMB Code Security as FBI Tallies $20.9B Losses

Image
Cyfendo Targets SMB Code Security as FBI Tallies $20.9B Losses

Mountain View – October 15, 2026 -- Cyfendo, a Silicon Valley application-security startup, has launched an AI platform that investigates software vulnerabilities and prepares tested patches for small businesses, as the FBI's 2025 Internet Crime Report recorded about $20.88 billion in reported losses across 1,008,597 complaints.

Cyfendo reports four critical issues per scanned codebase

According to Cyfendo's own scan data, the company finds an average of four critical-severity issues per codebase, and roughly seven in ten findings are rated high or critical. The company states these results come from projects it scanned, not a representative survey of business applications.

CGI: Frontier AI Shifts Cyber Bottleneck to Executive Decision Speed

Image
CGI: Frontier AI Shifts Cyber Bottleneck to Executive Decision Speed

Global – October 15, 2026 -- The main constraint on cyber defense is moving from vulnerability discovery to organizational decision speed, according to CGI's Pierre Le Calvez, as frontier models such as Anthropic's Claude Mythos and OpenAI's GPT-5.6 Sol advance.

Approval delays outpace detection in security operations

In a blog titled "Defending at the speed of frontier AI: Lessons from the Fable shutdown and what to do in the next 60 days," Le Calvez argues that AI-assisted tools now surface vulnerabilities within minutes and clarify their impact within hours. The delays now sit in approval processes, competing business priorities, resource constraints and fragmented ownership rather than inside the security operations center.

Resilient organizations share five operating traits

The blog lists the characteristics of resilient organizations:

CompTIA: 98% of Firms Rank AI Risk Management Essential

Image
CompTIA: 98% of Firms Rank AI Risk Management Essential

Downers Grove, Ill. – October 15, 2026 -- Some 98% of companies surveyed by CompTIA say risk management is important within organizational AI policies, as the focus of enterprise AI shifts from adoption to execution risk, according to the trade group's new research brief "Practical Implications of AI Safety."

About six in 10 organizations move toward enterprise-wide AI implementation

CompTIA's "Corporate AI Adoption" report found that roughly 60% of organizations are moving from experimentation and individual productivity use cases toward enterprise-wide deployment. Cybersecurity concerns rank as the second-largest challenge to AI adoption. Only finding the right balance between human employees and AI-powered tools and agents ranks higher.

Security-related policy elements draw near-universal support

Among surveyed companies, 96% cited data protection and privacy as important, and 95% cited governance. Risk management led at 98%.