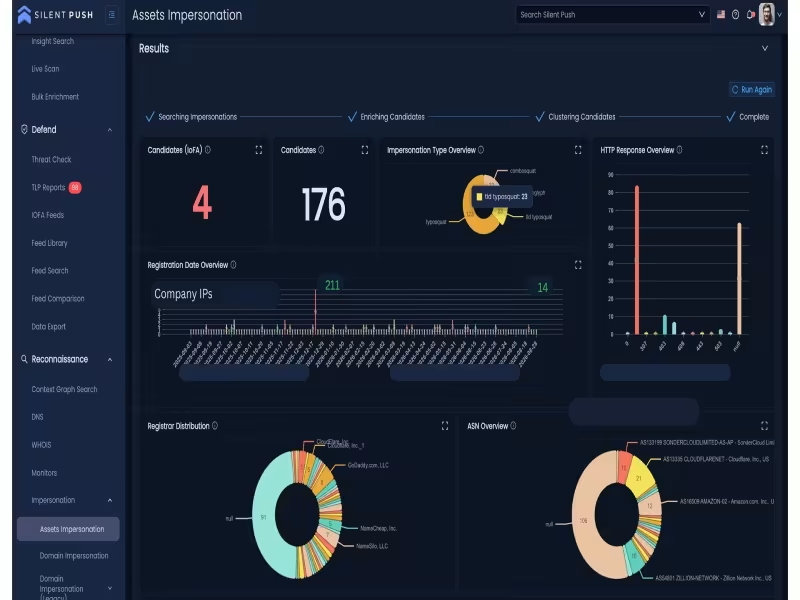
Reston, Va. – September 12, 2026 -- Silent Push has launched version 6.1 of its preemptive cyber defense platform, introducing a fully automated Brand and Infrastructure Impersonation engine that continuously hunts look-alike domains before they are weaponized in phishing campaigns.
Rebuilt engine scores and clusters look-alike domains for automated takedown
The new engine scores look-alike domains by risk, enriches them with registrar and hosting context, clusters them by threat actor, and exports the results as takedown evidence. Once configured, the system runs on an ongoing basis, reporting newly discovered impersonation infrastructure to security teams without manual re-scanning.
Gartner frames brand abuse as a formal intelligence requirement, not a marketing issue
Gartner's April 2026 research note, "Align Cyberthreat Intelligence to Business Priorities for Stronger SecOps" by Jonathan Nunez, lists "Brand Abuse and Phishing Infrastructure" as a core intelligence requirement, asking security operations teams to identify malicious domains and impersonation campaigns leveraging their brand before they scale. Silent Push 6.1 is designed to answer that question ahead of the first phishing email being sent.
Revolut's threat intelligence lead reports detections months ahead of other tools
Vladimir Krupnov, Threat Intelligence Lead at Revolut, said Silent Push isolates impersonated domains with detection timelines months ahead of competing tools, giving his team early-action intelligence to protect the business. Ken Bagnall, Co-Founder and CEO of Silent Push, said the new engine turns attacker infrastructure data against the attackers themselves, identifying imposters before look-alike domains are used.
New integrations extend the platform into SOAR, browsers, and AI workflows
Silent Push 6.1 adds integration with Palo Alto Cortex XSOAR for automated playbooks, a Chrome Extension for in-browser investigation, and an MCP Server exposing platform data to AI assistants and agentic workflows via the Model Context Protocol. An updated TAXII Server now supports bidirectional STIX/TAXII intelligence sharing, while new TLP: AMBER+STRICT reporting restricts custom analyst reports to designated recipients only.
Advanced Pivot Control and My Assets speed analyst investigations
Insight Search now processes domains, IPs, ASNs, subnets, and HTML titles in a single query, while Total View adds a PADNS timeline, IP certificates, one-click PDF export, and screenshot date filtering. The My Assets feature lets analysts build a reusable, tagged inventory of owned domains, IP ranges, ASNs, and TLDs for one-click use across the platform.
Platform interface expands into Korean and Spanish, with Japanese pending
Silent Push 6.1's interface is now localized in Korean and Spanish alongside English, with navigation and guidance translated per user while underlying threat data remains unchanged. Japanese localization is planned shortly, with additional languages available on customer request.