Ai Security

Oracle: AI Now Writes 70% of Its Code, Adds Google TPUs to OCI

Image
Oracle: AI Now Writes 70% of Its Code, Adds Google TPUs to OCI

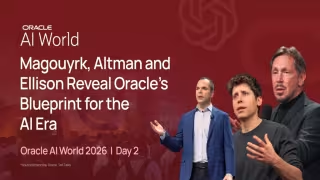
Las Vegas – October 29, 2026 -- More than 70% of Oracle's code is now written by AI, CEO Clay Magouyrk told attendees on Day 2 of Oracle AI World 2026, as the company paired the disclosure with security, chip and application announcements.

Oracle cuts support resolution from 3.5 hours to 16 minutes

Magouyrk presented internal results before announcing any product. Support requests that once took 3.5 hours now resolve in 16 minutes. Product ideas that previously took nine months to reach customers now take six weeks. Vulnerabilities are found and fixed ten times faster than six months ago.
Malicious LiteLLM 1.107.0 on PyPI Steals AI Keys, Installs RAT

Image
Malicious LiteLLM 1.107.0 on PyPI Steals AI Keys, Installs RAT

Global – October 29, 2026 -- A malicious version of LiteLLM, version 1.107.0, was published to PyPI on October 29, 2026. It bundles a credential-stealing infostealer with a remote access trojan (RAT), according to OX Security. It is the second hijacking of the AI gateway this year, and PyPI has since quarantined the release.

Malware hides in the wheel package, not the source repository

The attacker injected the code only into the wheel package, so a review of the repository or the clean source would show nothing wrong. Stolen data goes to litellm[.]dev, a domain the attacker bought that can pass for a legitimate LiteLLM address. In March, versions 1.82.7 and 1.82.8 were compromised in the TeamPCP campaign, but this attack used different tooling and infrastructure.

OX Launches Agent Activity to Trace and Control AI Agents

Image
OX Launches Agent Activity to Trace and Control AI Agents

Global – October 29, 2026 -- OX has launched Agent Activity in early access, giving security teams step-by-step runtime visibility into AI agent sessions across its OX.VibeSec and OX.Cloud platforms, with more than 100 built-in guardrail policies.

Agent Activity traces each session from prompt to data access

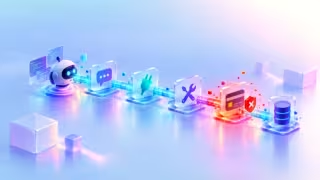
For every agent session, security teams can follow the full chain of actions from start to finish. The tool records prompts and responses, the MCP servers and tools the agent called and in what order, and whether the agent held read or write access. That distinction separates an agent that views a ticket from one that modifies it, or one that reads Slack from one that posts to it.

It also flags when an agent interacts with PII, secrets, tokens, or financial data, and when that data risks leaving where it belongs.

QKS Group Names Radware Leader in Q4 2026 Bot Management SPARK Matrix

Image
QKS Group Names Radware Leader in Q4 2026 Bot Management SPARK Matrix

PUNE, India – October 22, 2026 -- QKS Group named Radware a technology leader in its global SPARK MatrixTM: Bot Management, Q4 2026, with strong ratings across technology excellence and customer impact. The study ranks leading vendors and assesses market dynamics, major trends, vendor landscape and competitive positioning.

Radware shifts bot detection from static signatures to intent analysis

Sofia Ali, Principal Analyst at QKS Group, said Radware has moved detection away from static signatures and score-based rules toward intent-driven analysis of automation behavior. Its engine combines three elements in one self-learning framework: pre-emptive blocking through the ERT Active Attackers Feed, AI-based behavioral analysis across hundreds of signals, and real-time signature generation. According to Ali, the framework catches evasive, human-like bots with less manual tuning.

Chainguard Launches Harness AI Bug Hunter on Claude Marketplace

Image
Chainguard Launches Harness AI Bug Hunter on Claude Marketplace

Seattle – October 14, 2026 -- Chainguard has launched Chainguard Harness, a cyber harness that runs frontier AI models such as Anthropic's Claude Mythos 5.1 against a live build of a customer's application and delivers only reproduced vulnerabilities, each paired with an engineer-reviewed fix. The product is available through the Claude Marketplace by Anthropic, so enterprises can buy it with their existing Anthropic commitment.

Harness tests running applications in isolated microVMs instead of scanning static code

Harness connects to a team's repository through the Guardener GitHub app, builds the application as it ships, and boots it in an isolated microVM. A frontier model then probes the running instance the way an attacker would. Chainguard says this approach surfaces logic flaws, injection paths and resource exhaustion bugs that appear only at runtime and that traditional static scanners miss.

Japan's 2026 Cyber Incidents Top 2025 Total in Nine Months

Image
Japan's 2026 Cyber Incidents Top 2025 Total in Nine Months

Dallas – October 13, 2026 -- Japan recorded more publicly disclosed cybersecurity incidents in the first nine months of 2026 than in all of 2025, according to TrendAITM Forward-Looking Threat Research data. TrendAITM, the enterprise business unit of Trend Micro Incorporated (TYO: 4704), issued a threat advisory for Japanese organizations after a senior ruling-party lawmaker declared that "cyberspace is in a state of emergency."

September incidents rise 37% from July to 86

September alone saw 86 incidents, about 18% more than August and 37% more than July. Masaaki Taira, who chairs the Liberal Democratic Party's National Cybersecurity Strategy Headquarters, made the emergency statement. The headquarters met on Oct. 9 and called on the government to strengthen public-private cooperation.

NVIDIA Launches Open Agent Safety Platform With CrowdStrike

Image
NVIDIA Launches Open Agent Safety Platform With CrowdStrike

Austin – October 12, 2026 -- NVIDIA introduced the NVIDIA Open Agent Safety Platform, an open source platform and reference design that applies multi-layered security controls across the software, runtime and infrastructure where AI agents operate, with CrowdStrike collaborating on the effort.

NVIDIA Sentry enforces policy from BlueField-4 DPUs and can quarantine agents in milliseconds

At the software layer, NVIDIA OpenShell provides an open source secure runtime that governs how agents execute, what they can access and where inference occurs. NVIDIA Sentry adds an independent watchdog running on NVIDIA BlueField-4 DPUs. It uses NVIDIA DOCA for out-of-band, in-silicon monitoring of agent activity and policy enforcement.

TrendAI Pairs Threat Intelligence With NVIDIA's Agent Safety Platform

Image
TrendAI Pairs Threat Intelligence With NVIDIA's Agent Safety Platform

Dallas – September 28, 2026 -- TrendAI, the AI security business unit of Trend Micro Incorporated (TYO: 4704; TSE: 4704), announced support for the NVIDIA Agent Safety Platform, combining hardware-level detection on NVIDIA BlueField DPUs with Zero Day Initiative threat intelligence to help enterprises move autonomous agent fleets from pilot programs into production.

NVIDIA's Agent Safety Platform Enforces Policy Through BlueField-4 DPUs Outside the Agent's Reach

NVIDIA's OpenShell component enforces policy outside an agent's execution environment, preventing it from being prompted away or bypassed, while BlueField-4 DPUs and NVIDIA DOCA add a security layer in silicon that operates independently of the host system. TrendAI positions its platform as the layer that determines what that enforced policy should be, providing visibility into agent behavior and the threat detection needed to act on it.