Cybersecurity

Study: 37% of Known Cyber Threats Have No Working Detection Coverage

Dallas and Tel Aviv – September 24, 2026 -- Enterprises have working detections for only 63% of the cyber threats they have already identified as relevant, leaving more than a third of known risks operationally uncovered, according to new research from Conifers based on an analysis of 14,652 detections in live enterprise environments.

The report, titled The Detection Blind Spot, found that detection coverage extended to just 64% of the MITRE ATT&CK techniques relevant to each environment studied. Nearly half of all detections examined, 47%, required attention before they could be trusted to function as intended, despite appearing as deployed or healthy in standard inventory-based reporting.
Discern Security Integrates With Jamf for AI Asset Discovery on Mac Fleets

Sunnyvale, Calif. – September 24, 2026 -- Discern Security has launched an integration with Jamf that turns existing device inventory data into visibility on AI and Shadow AI tools running across managed Mac fleets, the companies announced. The integration is available now on the Jamf Marketplace.

Integration requires no new endpoint software

The system uses a read-only API role and the Jamf agent already deployed on managed devices, avoiding additional installations. It draws on Jamf Pro data spanning computers, computer groups, OS X configuration profiles, patch policies, software title configurations, mobile devices, applications, users, LDAP servers, SSO, and webhooks.

KuCoin Wallet Services Reach CCSS Level 3, Top Security Tier

Image
KuCoin Wallet Services Reach CCSS Level 3, Top Security Tier

Providenciales – – September 24, 2026 -- KuCoin has upgraded its Wallet Management Services from CCSS v8.1 Level 2 to CCSS v8.1 Level 3, the highest tier of the Cryptocurrency Security Standard, the exchange announced.

KuCoin secures full-system certification under the CCSS v8.1 framework

The Level 3 rating, assessed under the same v8.1 standard as the prior certification, verifies stronger controls across the full cryptographic key lifecycle, from generation and storage to access, backup and recovery.

New controls target key-compromise response and personnel access

Compared with Level 2, the Level 3 certification requires greater separation of responsibilities, stricter access and personnel controls, regular testing of key-compromise response procedures, broader independent assurance, and continual backup of operational logs. KuCoin said the measures reduce single points of failure and improve traceability and resilience.

Kigen Achieves First GSMA eSA Certification for Automotive eSIMs

Image
Kigen Achieves First GSMA eSA Certification for Automotive eSIMs

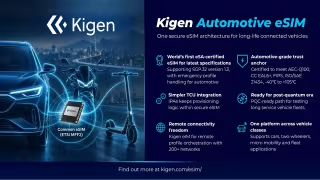
Cambridge, England – September 23, 2026 -- Kigen has become the first company to achieve GSMA eUICC Security Assurance (eSA) certification for an automotive eSIM supporting SGP.32 v1.3, GSMA's latest IoT eSIM specification, giving connected-vehicle manufacturers a standards-current security platform for fleets requiring decade-plus service life.

The certification pairs Kigen's eSIM OS with Infineon's TEGRION SLI22 automotive security controller. It extends Kigen's certified portfolio across the TEGRION SLx22 chip family into three products: Automotive (SLI22), Consumer (SLC22, supporting SGP.22 v2.7), and Industrial IoT (SLM22, supporting SGP.32 v1.3). All three share a common OS, hardware platform, development tools and management stack, letting OEMs apply one security architecture across infotainment, telematics and headless vehicle systems.

Chainguard Becomes CVE Numbering Authority to Fight AI-Found Flaws

Image
Chainguard Becomes CVE Numbering Authority to Fight AI-Found Flaws

New York – September 22, 2026 -- Chainguard has been authorized by the CVE Program as a CVE Numbering Authority (CNA), granting it the power to assign official vulnerability identifiers for qualifying open source flaws surfaced through its Athena coalition.

Chainguard gains authority to assign CVE identifiers for unclaimed open source flaws

The CNA scope covers cases where upstream maintainers have already fixed a flaw without issuing an identifier, where no maintainer remains to assign one, or where no more specific CNA covers the affected project. Chainguard's CVE Records will defer to maintainers and project-specific CNAs wherever they exist.

Siemba Launches Global Partner Program With Tiered Margins, White-Label Delivery

Image
Siemba Launches Global Partner Program With Tiered Margins, White-Label Delivery

Atlanta – September 22, 2026 -- Siemba, a continuous offensive security provider, has launched Siemba Pride, a formal global partner program offering deal registration, co-sell support, tiered margins, and white-label delivery on its AI-driven continuous threat exposure management (CTEM) platform.

Three partner pillars target distinct channel roles

Siemba Pride organizes partners into three categories. Enablers are systems integrators that deploy and operationalize the platform inside enterprise environments. Amplifiers cover MSSPs, agencies, resellers, and procurement networks that bring Siemba to new customers through their own channels. Enhancers are ISVs and technology platforms that integrate with Siemba via APIs and co-engineered workflows.

ScamAdviser's Watchmen Wins Scam Fighter Award at GASA Summit

Image
ScamAdviser's Watchmen Wins Scam Fighter Award at GASA Summit

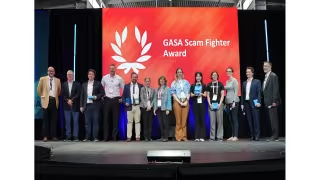
San Francisco – September 22, 2026 -- ScamAdviser's Watchmen platform won the Scam Fighter Award at the Global Anti-Scam Summit (GASS) America 2026, organized by the Global Anti-Scam Alliance (GASA) in San Francisco, for its role in cutting fraud detection-to-takedown times from weeks to under 8 hours.

Watchmen deployments contributed to a 38% drop in investment scam financial losses

In deployments with financial regulators, law enforcement agencies, and municipal governments, Watchmen demonstrated national-level impact, including a 38% reduction in the share of investment scam financial losses. The system uses multi-layered filtering, expert rule engines, and Large Language Model (LLM) semantic analysis to monitor corporate communication channels and social media platforms for brand impersonation, triggering automated takedown mechanisms once threats are confirmed.

Siemba Launches MCP Server to Run Pentests via AI Chat

Image
Siemba Launches MCP Server to Run Pentests via AI Chat

Atlanta – September 22, 2026 -- Siemba has launched general availability of Siemba MCP, a Model Context Protocol server that lets security and engineering teams run penetration tests and generate finished security analysis by chatting directly with AI assistants, eliminating the need for a separate dashboard login.

Six packaged skills replace manual dashboard analysis

Siemba MCP ships as a single plugin containing a connector and six named skills: Test Analysis, Kill Chain, Critical Briefing, Remediation Plan, Attack Surface, and CISO Report. Test Analysis reads login screenshots to diagnose failed authenticated test runs caused by bad credentials or unexpected multi-factor prompts. Kill Chain maps individual findings into full attack paths, rating each chain by its weakest link rather than raw severity and naming the single fix that breaks the most chains at once.

Palo Alto Networks Launches Continuous AI Defense with Anthropic, OpenAI

Image
Palo Alto Networks Launches Continuous AI Defense with Anthropic, OpenAI

Santa Clara, Calif. – September 22, 2026 -- Palo Alto Networks has launched Unit 42 Continuous Frontier AI Defense, a new agentic offensive security service built on Anthropic's Claude Mythos 5 and OpenAI's GPT-5.6-Cyber models, aimed at helping enterprises find and fix exposures before attackers exploit them at machine speed.

The service responds to a shift in attacker capability: threat actors using AI have compressed breach cycles by nearly 97% in some cases, cutting the time from vulnerability discovery to exploitation from weeks to hours, according to Palo Alto Networks.

Ridgeway Pharmacy Discloses Third-Party Website Breach Exposing Patient Data

Victor, Montana – – September 21, 2026 -- Ridgeway Pharmacy, Ltd. has confirmed that a vulnerability in its vendor-supported website allowed an unauthorized third party to gain elevated access, potentially exposing patient names, dates of birth, addresses, prescription and health information, insurance details, and, for some individuals, payment card data.

Ridgeway confirms breach originated in vendor-managed site, not internal systems

The pharmacy said the compromise was limited to its externally developed website and did not touch Ridgeway's own internal infrastructure. External cybersecurity and forensic specialists were brought in after operational irregularities were first detected on the site.